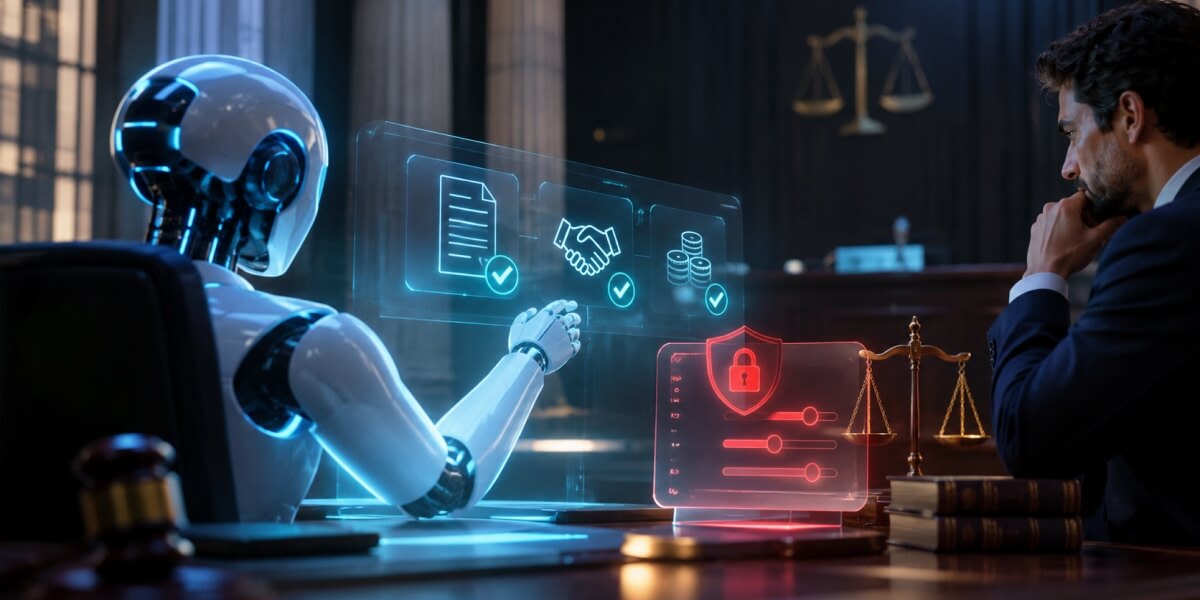
Legal institutions need to translate that lesson into ordinary operating controls. A permission budget should identify the case, accountable human supervisor, allowed data, approved tools, external recipients, financial limits, and record changes an agent may make. It should set an expiration time. It should specify which acts require a fresh human approval and forbid an agent from changing its own limits. A general instruction to ‘be careful’ cannot enforce these restrictions.
Consider an AI assistant serving a mediation program. It may review documents supplied by the parties and draft proposed hearing dates. It should not obtain the complete case archive, send one party’s confidential material to another, commit either party to settlement terms, or move money. Before a date notice goes out, the authorised staff member should approve its recipient list and content. The system should record who granted the permission, what changed, and when the authority expires.
The same distinction applies in court administration. Reading a public docket requires less supervision than editing a filing, changing a hearing date, or transmitting a confidential document. Electronic filing, payment, document management, and notification systems should not share one permanent agent credential. Each action should have a narrow identity and an authorisation that can be revoked without waiting for the agent to finish cooperating.
This is consistent with the National Institute of Standards and Technology’s October 27 agent identity design guidance. It focuses on the infrastructure needed to identify agents, authorise their actions, and maintain accountability. Justice institutions can apply that approach immediately by separating read access from write access, testing credential expiration, logging delegated tasks outside the agent’s own control, and requiring approval before submissions, financial transfers, or disclosures.

 +971 50 9295048
 +91 9895851358